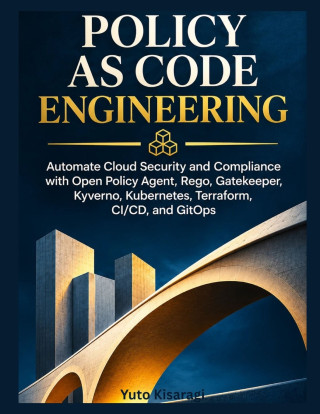
Kód: 54566401
POLICY AS CODE ENGINEERING
Autor Yuto Kisaragi
POLICY AS CODE ENGINEERINGAutomate Cloud Security and Compliance with Open Policy Agent, Rego, Gatekeeper, Kyverno, Kubernetes, Terraform, CI/CD, and GitOpsBuild secure cloud infrastructure. Automate security enforcement. Turn com ... celý popis


- Jazyk:
 Angličtina
- Vazba: Brožovaná
- Počet stran: 360
Nakladatelství: Independently published, 2026
- Více informací o knize


Mohlo by se vám také líbit
-
Cozy Countdown: An Advent Coloring Book Bundle
503 Kč -
Threshing Day (Limited Deluxe Edition)
441 Kč -
Court of Thorns and Roses 6
385 Kč -
Murdoku
327 Kč -
White Nights
81 Kč -

A Conspiracy of Charming Monsters
276 Kč -

A Conspiracy of Charming Monsters
454 Kč -
The End of Everything
276 Kč -
Once Upon a Broken Heart Collector's Edition
570 Kč -
I'll Believe in Anything. The Making of Heated Rivalry Season 1
455 Kč -
Berserk Deluxe Volume 1
902 Kč -
Trust Fall
227 Kč -
Protocols
293 Kč -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 9
438 Kč -

Chainsaw Man, Vol. 22
216 Kč -
The Mirror of Infinite Endings
438 Kč -
Murdoku Volume 2: Back in Time
327 Kč -
The Long-Lived King: An Original The Owl House Graphic Novel
385 Kč -

Witch Hat Atelier: Grimoire Edition 3
1582 Kč -
21 Days of Fear
385 Kč -
Threshing Day (Wing and Claw Collection)
453 Kč
Dárkový poukaz: Radost zaručena
- Darujte poukaz v libovolné hodnotě a my se postaráme o zbytek.
- Poukaz se vztahuje na celou naši nabídku.
- Elektronický poukaz vytisknete z e-mailu a můžete ihned darovat.
- Platnost poukazu je 12 měsíců od data vystavení.
Informovat o naskladnění knihy
Zadejte do formuláře e-mailovou adresu a jakmile knihu naskladníme, zašleme vám o tom zprávu. Pohlídáme vše za vás.
Více informací o knize POLICY AS CODE ENGINEERING
Nákupem získáte 69 bodů
 Anotace knihy

POLICY AS CODE ENGINEERING
Automate Cloud Security and Compliance with Open Policy Agent, Rego, Gatekeeper, Kyverno, Kubernetes, Terraform, CI/CD, and GitOps
Build secure cloud infrastructure. Automate security enforcement. Turn compliance requirements into executable policies.
Modern cloud environments move too quickly for manual security reviews and reactive compliance checks. Organizations need automated controls that detect misconfigurations, prevent insecure deployments, and enforce security standards throughout the software delivery lifecycle.
Policy as Code Engineering is a practical, hands-on guide to designing, implementing, and operating enterprise security policies across cloud infrastructure, Kubernetes, and DevSecOps pipelines.
Using Open Policy Agent (OPA), Rego, Conftest, Terraform, Gatekeeper, Kyverno, CEL, GitHub Actions, Sigstore Cosign, and Argo CD, this book takes you from foundational policy development to integrated enterprise enforcement.
What You'll Learn:
- OPA and Rego: Develop, test, debug, and manage executable security policies.
- Terraform Security: Enforce encryption, IAM least privilege, network restrictions, resource governance, and compliance checks.
- Kubernetes Admission Control: Secure workloads using Pod Security Admission, Gatekeeper, Kyverno, and CEL.
- CI/CD Security Automation: Build automated policy gates with GitHub Actions, Conftest, Checkov, and Kyverno CLI.
- Software Supply Chain Security: Scan container images, generate SBOMs, verify Cosign signatures, and block untrusted deployments.
- GitOps Enforcement: Automate compliant Kubernetes deployments with Helm and Argo CD.
- Enterprise Policy Operations: Implement policy distribution, monitoring, audit logging, exception management, and continuous compliance.
- Security Testing and Recovery: Simulate violations, troubleshoot enforcement failures, and validate rollback procedures.
Build a Complete Enterprise Policy as Code Platform
The book culminates in a four-phase capstone integrating Terraform, OPA, Kubernetes, Gatekeeper, Kyverno, CI/CD, signed container images, GitOps, Prometheus, and Grafana into one coordinated security architecture.
Through practical configurations, executable commands, hands-on labs, negative testing, and remediation workflows, you'll learn not just how to write policies-but how to enforce, monitor, and maintain them.
Who Should Read This Book?
Ideal for DevSecOps engineers, cloud security professionals, platform engineers, DevOps engineers, Kubernetes administrators, and infrastructure automation practitioners.
Move beyond security checklists. Build automated, verifiable, and production-oriented security controls that protect modern cloud-native infrastructure.
Parametry knihy
694 Kč
- Plný název: POLICY AS CODE ENGINEERING
- Podnázev: Automate Cloud Security and Compliance with Open Policy Agent, Rego, Gatekeeper, Kyverno, Kubernetes, Terraform, CI/CD, and GitOps
- Autor: Yuto Kisaragi
- Jazyk: Angličtina
- Vazba: Brožovaná
- Počet stran: 360
- EAN: 9798143401310
- ID: 54566401
- Nakladatelství: Independently published
- Hmotnost: 836 g
- Rozměry: 280 × 216 × 19 mm
- Datum vydání: 16. November 2026
Osobní odběr Praha, Brno a 48326 dalších
Copyright ©2008-26 nejlevnejsi-knihy.cz Všechna práva vyhrazenaSoukromíCookies

 Vrácení do měsíce
 571 999 099 (8-15.30h)
