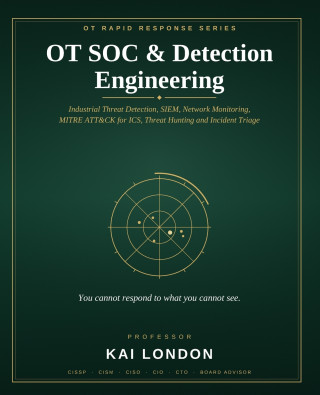
Kód: 53735319
OT SOC & Detection Engineering
Autor Kai London
Build detections around trusted-state change, asset context and process consequence - then validate them safely before relying on them in production. This field manual equips OT security operations teams with practical guidance on ... celý popis


- Jazyk:
 Angličtina
- Vazba: Brožovaná
- Počet stran: 802
Nakladatelství: Independently published, 2026
- Více informací o knize


Mohlo by se vám také líbit
-
Threshing Day (Wing and Claw Collection)
400 Kč -
Murdoku
334 Kč -
Threshing Day (Limited Deluxe Edition)
473 Kč -
Berserk Deluxe Volume 1
879 Kč -
What Happened Yesterday
380 Kč -
White Nights
89 Kč -
Berserk Deluxe Volume 2
943 Kč -
Berserk Deluxe Volume 3
779 Kč -
Court of Thorns and Roses 6
358 Kč -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 8
427 Kč -
Onyx Storm (Deluxe Limited Edition) (The Empyrean, 3)
527 Kč -
Dancing The Dream
482 Kč -
Yesteryear
335 Kč -
Kid's Box New Generation Level 2 Activity Book with Digital Pack British English
251 Kč -
Murdoku
362 Kč -
21 Days of Fear
381 Kč -
Kid's Box New Generation Level 3 Activity Book with Digital Pack British English
251 Kč -
The Courage To Be Disliked
206 Kč -
Kid's Box New Generation Level 1 Activity Book with Digital Pack British English
251 Kč -
Witch Hat Atelier: Grimoire Edition 1
779 Kč -
The Count of Monte Cristo
221 Kč
Dárkový poukaz: Radost zaručena
- Darujte poukaz v libovolné hodnotě a my se postaráme o zbytek.
- Poukaz se vztahuje na celou naši nabídku.
- Elektronický poukaz vytisknete z e-mailu a můžete ihned darovat.
- Platnost poukazu je 12 měsíců od data vystavení.
Více informací o knize OT SOC & Detection Engineering
Nákupem získáte 297 bodů
 Anotace knihy

Build detections around trusted-state change, asset context and process consequence - then validate them safely before relying on them in production. This field manual equips OT security operations teams with practical guidance on SIEM design, network monitoring, MITRE ATT&CK for ICS mapping, threat hunting and incident triage, closing with a reusable operating pack of maturity models, evidence catalogues and control questions. Written for defensive cybersecurity, engineering assurance, resilience, audit and governance use by teams building or maturing an industrial security operations capability.
Parametry knihy
2974 Kč
- Plný název: OT SOC & Detection Engineering
- Podnázev: Industrial Threat Detection, SIEM, Network Monitoring, ATT&CK for ICS, Threat Hunting and Incident Triage
- Autor: Kai London
- Jazyk: Angličtina
- Vazba: Brožovaná
- Počet stran: 802
- EAN: 9798171265090
- ID: 53735319
- Nakladatelství: Independently published
- Hmotnost: 1354 g
- Rozměry: 235 × 191 × 40 mm
- Datum vydání: 01. September 2026
Osobní odběr Praha, Brno a 48132 dalších
Copyright ©2008-26 nejlevnejsi-knihy.cz Všechna práva vyhrazenaSoukromíCookies

 Vrácení do měsíce
 571 999 099 (8-15.30h)
