Kód: 54515717
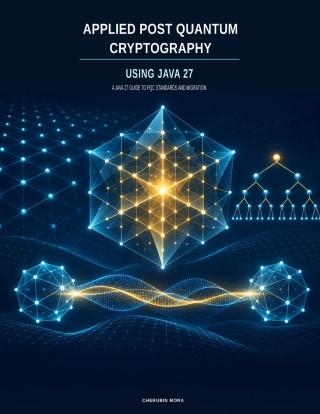
Applied Post Quantum Cryptography Using Java 27
Autor Cherubin Mora
Cryptographic migration takes years, while sensitive information may need protection for decades. Applied Post Quantum Cryptography Using Java 27 gives Java developers a practical guide to the quantum threat and the standards desi ... celý popis


- Jazyk:
 Angličtina
- Vazba: Brožovaná
- Počet stran: 108
Nakladatelství: Independently published, 2026
- Více informací o knize


Mohlo by se vám také líbit
-
Threshing Day (Limited Deluxe Edition)
441 Kč -
Cozy Countdown: An Advent Coloring Book Bundle
514 Kč -
Court of Thorns and Roses 6
348 Kč -
Murdoku
342 Kč -
White Nights
82 Kč -
Trust Fall
227 Kč -

A Conspiracy of Charming Monsters
419 Kč -
I'll Believe in Anything. The Making of Heated Rivalry Season 1
460 Kč -
The Mirror of Infinite Endings
434 Kč -

A Conspiracy of Charming Monsters
276 Kč -
Once Upon a Broken Heart Collector's Edition
630 Kč -
The Long-Lived King: An Original The Owl House Graphic Novel
385 Kč -

Chainsaw Man, Vol. 22
230 Kč -
Jojo's Bizarre Adventure: Part 7--Steel Ball Run, Vol. 9
438 Kč -
Berserk Deluxe Volume 1
899 Kč -
Protocols
428 Kč -
Murdoku Volume 2: Back in Time
293 Kč -
The End of Everything
292 Kč -
21 Days of Fear
406 Kč -
Threshing Day (Wing and Claw Collection)
453 Kč -
How to Win at Chess, Next Level
506 Kč
Dárkový poukaz: Radost zaručena
- Darujte poukaz v libovolné hodnotě a my se postaráme o zbytek.
- Poukaz se vztahuje na celou naši nabídku.
- Elektronický poukaz vytisknete z e-mailu a můžete ihned darovat.
- Platnost poukazu je 12 měsíců od data vystavení.
Informovat o naskladnění knihy
Zadejte do formuláře e-mailovou adresu a jakmile knihu naskladníme, zašleme vám o tom zprávu. Pohlídáme vše za vás.
Více informací o knize Applied Post Quantum Cryptography Using Java 27
Nákupem získáte 502 bodů
 Anotace knihy

Cryptographic migration takes years, while sensitive information may need protection for decades. Applied Post Quantum Cryptography Using Java 27 gives Java developers a practical guide to the quantum threat and the standards designed to address it.
Explore ML-KEM key establishment, ML-DSA and SLH-DSA signatures, identity and certificate trust, hybrid key establishment, and TLS 1.3 integration. The examples use Java 27 JCA, JCE, and JSSE, with Bouncy Castle where needed. Symmetric encryption, hashing, and classical cryptography appear only to explain how PQC fits into deployed systems.
The book also covers PQC standards and algorithm status, provider and protocol support, certificate interoperability, harvest-now-decrypt-later risks, active attacks, and staged migration. Each example explains its assumptions and limits: a KEM does not authenticate a peer, algorithm availability does not establish module validation, and hybrid protocols must use defined combinations.
Written for developers comfortable reading Java, this book helps teams inventory quantum-vulnerable systems and prepare a safe, testable transition to post-quantum cryptography.
Parametry knihy
5022 Kč
- Plný název: Applied Post Quantum Cryptography Using Java 27
- Autor: Cherubin Mora
- Jazyk: Angličtina
- Vazba: Brožovaná
- Počet stran: 108
- EAN: 9798141699511
- ID: 54515717
- Nakladatelství: Independently published
- Hmotnost: 368 g
- Rozměry: 280 × 216 × 7 mm
- Datum vydání: 11. November 2026
Osobní odběr Praha, Brno a 48478 dalších
Copyright ©2008-26 nejlevnejsi-knihy.cz Všechna práva vyhrazenaSoukromíCookies

 Vrácení do měsíce
 571 999 099 (8-15.30h)
